SECURITY CODE REVIEW TRAINING
The on-demand version of our Web Security Code Review Training, designed for penetration testers, security engineers, AppSec engineers, and developers who want to master security code review. Louis walks you through real code, real CVEs, and the methodology he uses on every review, in short lessons you can watch at your own pace. Each module ends with an exercise to apply what you learned to a codebase of your choice.
107 short lessons across 14 modules, about 9.6 hours of video. Watch at your own pace and pause when Louis asks you to look at the code. Some modules end with a task: apply what you learned to a codebase of your choice. Lessons with a PentesterLab lab count as complete once you have solved the lab (labs marked optional are extra practice).
Not sure yet? Watch 4 lessons for free
Training a team? Buy in bulk or deploy it in your LMS.
There has never been a better time to learn security code review
One of the most valuable skills in security
Reading code to find vulnerabilities is one of the most valuable skills in AppSec, and one of the hardest to learn on your own. With the source you skip the guesswork of black-box testing: you see how authentication works, where authorization checks happen, and which assumptions developers made.
It takes more than one strategy
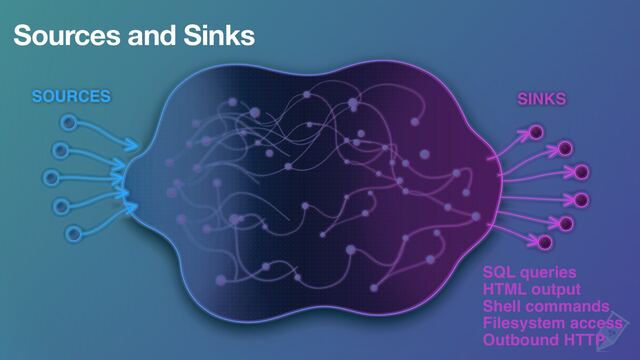
Good reviews are not just tracing sources to sinks. You learn when to compare two codebases, when to start from a CVE, when to work back from a dangerous function, and how to keep notes so a large, unfamiliar codebase stays manageable.
Real bugs, from real CVEs
The patterns behind real vulnerabilities, the gotchas that trip up experienced reviewers, and how to read a real CVE from the vulnerable code to the fix, so you recognise the same mistakes in the code you review.
AI helps, but it won't do it for you
AI can help you move faster once you know what you're doing, but it won't tell you where to look, and you need to know when it's wrong. That judgment comes from understanding the fundamentals.
That's what this course is for: the methodology I use on every review, the patterns behind real CVEs, and the strategies that go beyond source to sink. The better you can read code, the sharper every review you do becomes.
Course Content
1Getting StartedFree preview
-
 01-01
Welcome to the Course
Free preview
4 min
-
 01-02
Security Code Review Is About Code Quality
🔒
4 min
-
 01-03
A Skill Worth Learning, Even If You Don't Know the Language
🔒
8 min
-
 01-04
Give Your Review a Direction: Think Like a Villain, Then Read First
🔒
6 min
-
 01-05
Realistic Expectations, and How to Measure Progress
🔒
5 min
-
 01-06
Picking Targets to Learn, and Your Training Target
🔒
7 min
2Reading Code3 free previews
-
 02-01
Start with the Documentation
🔒
8 min
-
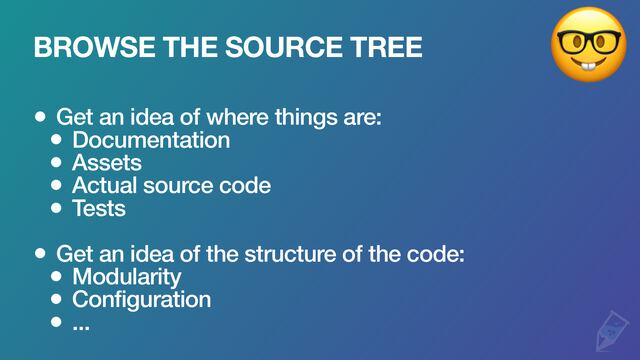 02-02
Browse the Source Tree, and Let DeepWiki Help
🔒
3 min
-
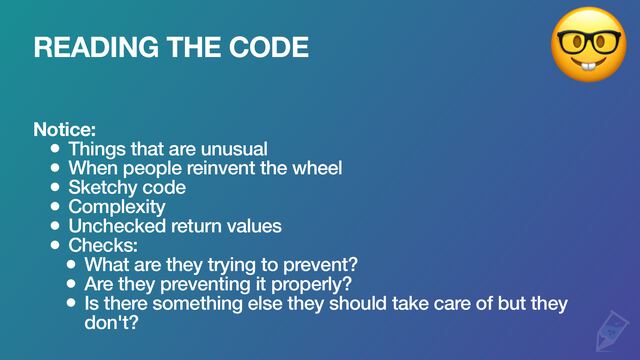 02-03
What to Notice When You Read Code
🔒
7 min
-
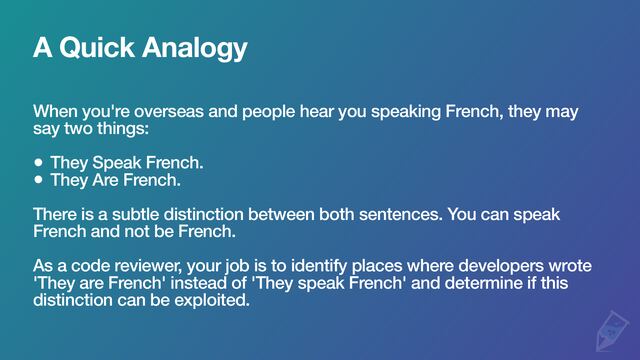 02-04
Speaking French vs Being French: Comments, Pragmas and Tests
1 lab
🔒
5 min
-
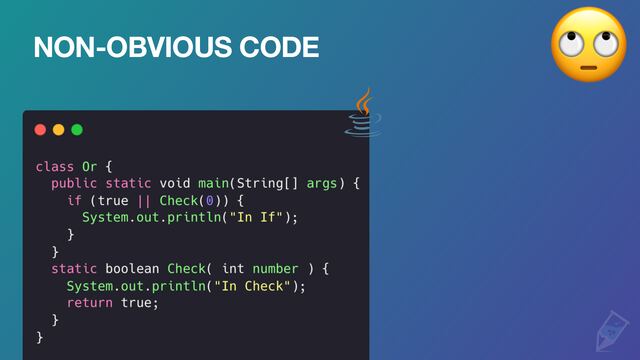 02-05
Code That Doesn't Do What It Seems: Short-Circuits, finally, Operators and Naked Returns
🔒
6 min
-
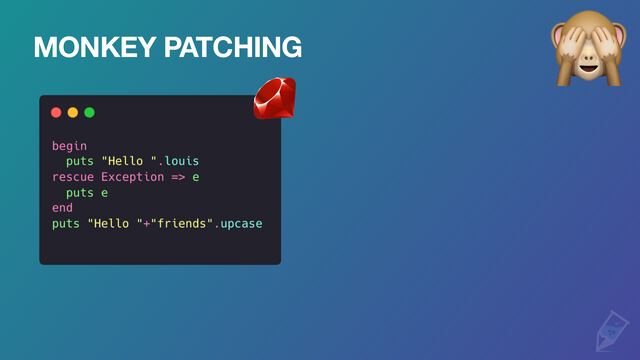 02-06
Metaprogramming: Monkey Patching, Magic Methods and eval
1 lab
🔒
5 min
-
 02-07
I Don't Like This Code #1: Three Buckets, and pgAdmin's Chunked Filter
Free preview
5 min
-
 02-08
I Don't Like This Code #2: A JWT Authorization Middleware
1 lab
🔒
5 min
-
 02-09
I Don't Like This Code #3: A CORS Check and the Empty Origin
Free preview
4 min
-
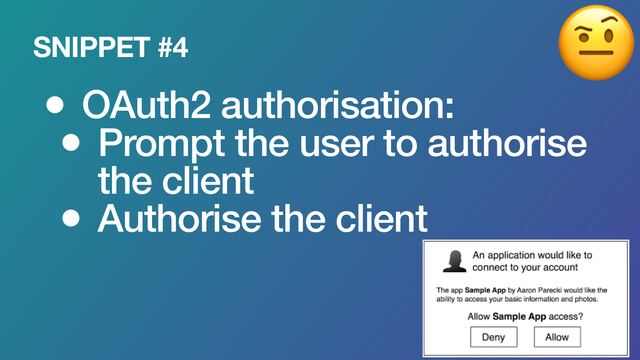 02-10
I Don't Like This Code #4 and #5: OAuth Routing and Astro's CSRF Check
1 lab
🔒
6 min
-
 02-11
I Don't Like This Code #6: An XSS Filter and the Live NodeList
Free preview
5 min
-
 02-12
Test Your Assumptions: REPLs, Docker, Then Your Target
🔒
5 min
- Browse the directory structure of your target.
- Read through the documentation available.
- Get familiar with some of the source code (do not grep for bugs, do not look for vulnerabilities).
- Are there any rules or conventions for the code?
- Find where "authentication" is done in the codebase: logging in, registration, password reset.
- Find a function in the source code of your target and test its behaviour.
3Keeping Notes
-
 03-01
Project Notes: Write Them So Reviews Compound
🔒
5 min
-
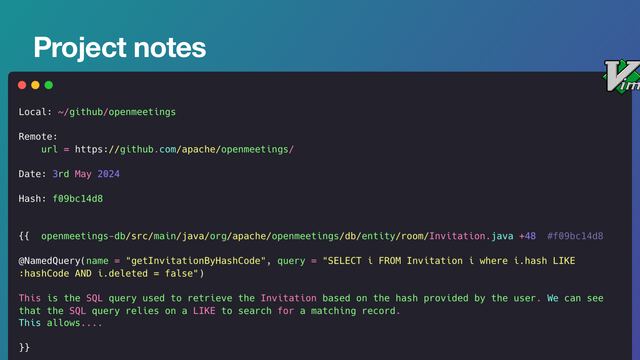 03-02
My Notes Template, Paper, Sequence Diagrams and Meta Notes
🔒
5 min
-
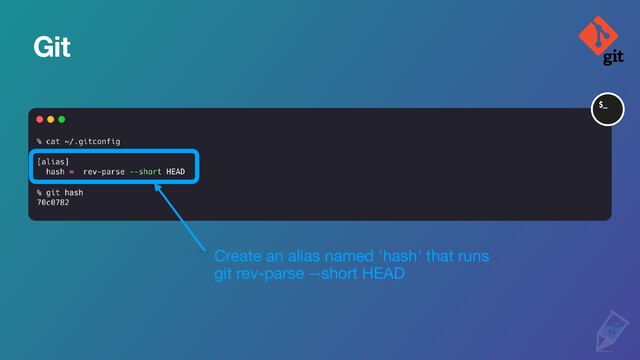 03-03
Watch Me Review a Codebase, Start to Finish
Bonus
🔒
18 min
- Setup your project notes for your target.
- Write anything relevant from what you learnt in the previous steps.
- Create your meta notes.
- Make a sequence diagram of the reset password flow of your target.
4Architecture, Routing and Attack Surface
-
 04-01
Inversion of Control, MVC and Conventions
🔒
5 min
-
 04-02
Routing: How URLs Map to Code
🔒
5 min
-
 04-03
Listing Routes, and Bugs You Can See in Them
🔒
4 min
-
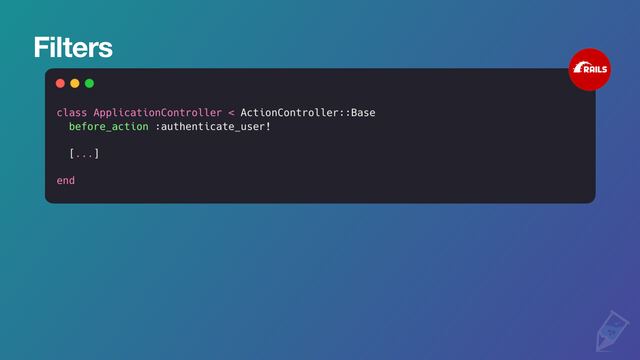 04-04
Filters and Middleware
🔒
6 min
-
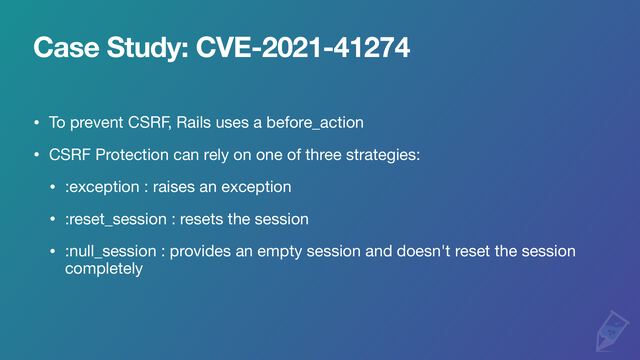 04-05
Order of Operations: Solidus's CSRF Bypass (CVE-2021-41274)
🔒
5 min
-
 04-06
Environments and Boilerplates, Then Your Target
1 lab
🔒
5 min
- List the available routes in your target.
- Deploy your target in a test environment.
- Is your target using some kind of filters/before_action to handle checks/authentication/authorisation/...
- Check how your target handles HEAD request, HTTP Routes, Path Manipulations, ...
5Data
-
 05-01
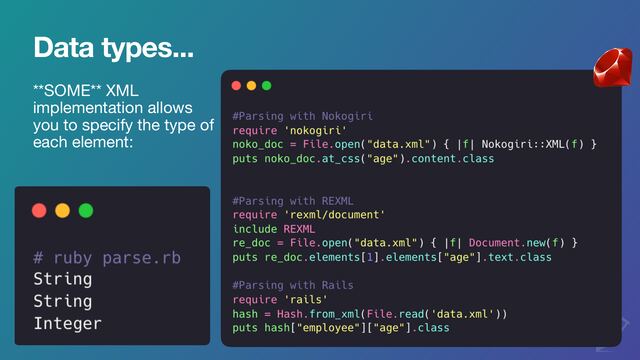
Everything Is Not a String
1 lab
🔒
3 min
-
 05-02
When Zero Matches the Token: Devise's Password Reset (2013)
🔒
7 min
-
 05-03
Same Bug, New Languages: MantisBT, GitLab and TypeScript
1 lab
🔒
7 min
-
 05-04
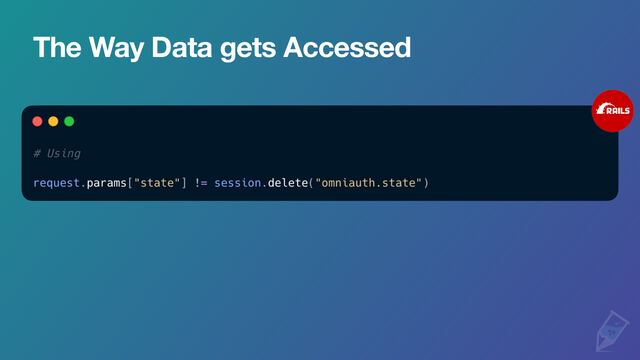
One Parameter, Many Sources: $_REQUEST and FormValue
1 lab
🔒
3 min
-
 05-05
Use It Once: Single-Use State in OmniAuth and WebAuthn
🔒
4 min
-
 05-06
Comparisons That Match Too Much: SQL LIKE and PHP's Loose ==
1 lab
🔒
6 min
-
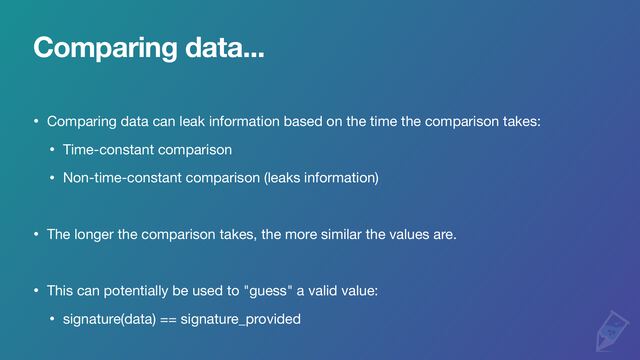 05-07
Timing Attacks: When a Comparison Leaks
1 lab
🔒
6 min
-
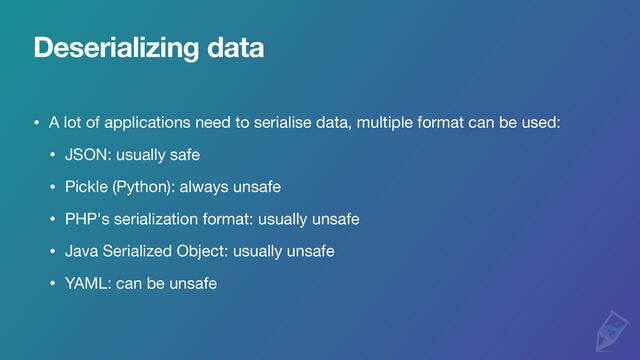 05-08
Deserializing Data, and XXE
1 lab
🔒
6 min
-
 05-09
Storing Data: Uniqueness and Collation
🔒
5 min
-
 05-10
When the Database Recycles IDs: Payload CMS (CVE-2025-4644)
🔒
4 min
-
 05-11
I Don't Like This Code, Round 2: play-with-docker's CORS and Apache Brooklyn
1 lab
🔒
5 min
-
 05-12
Round 2: auth0's JWT Check and a Command Filter
1 lab
🔒
6 min
-
 05-13
The Grand Finale: Apache Doris's Random Challenge
🔒
6 min
- Look at how data is handled in your application: retrieved from requests, generated, parsed.
6Patterns
-
 06-01
What a Pattern Is, and the First One: Hard-Coded Secrets and Bad Defaults
1 lab
🔒
4 min
-
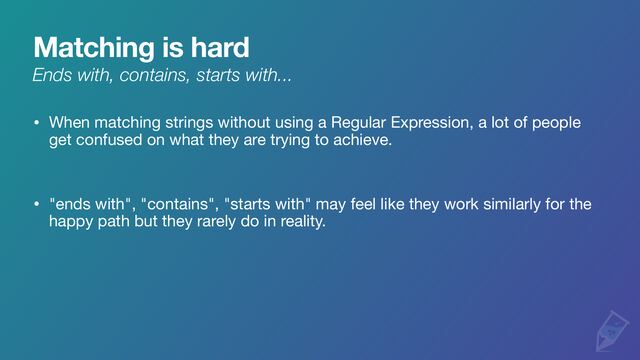 06-02
Matching Is Hard: contains, startsWith and Gradio's Path Check
🔒
3 min
-
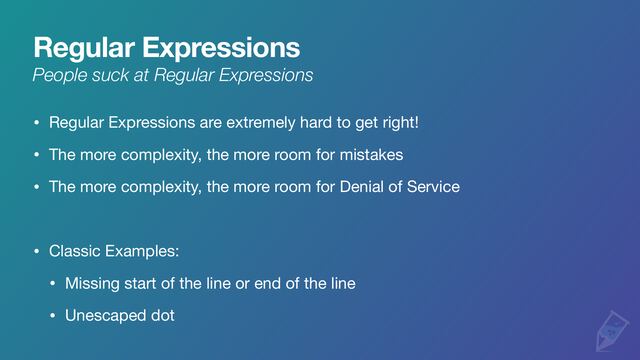 06-03
People Suck at Regular Expressions: Dots, Anchors and [A-z]
1 lab
🔒
4 min
-
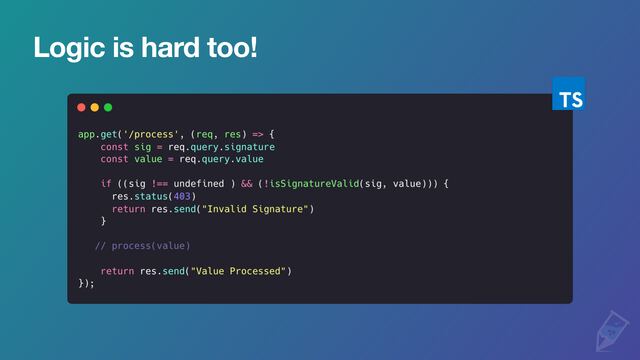 06-04
Logic Is Hard: Optional Checks, || vs && and Missing Returns
🔒
3 min
-
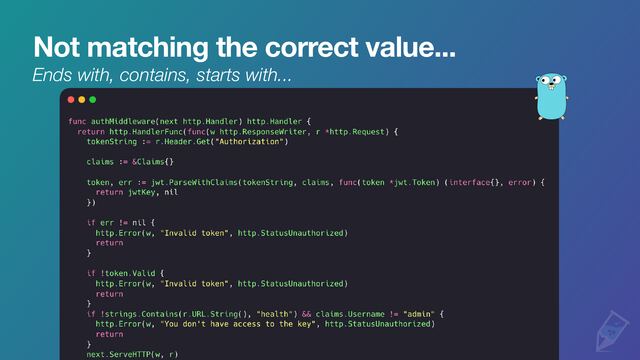 06-05
The Wrong Value, Then Your Turn: Bypass the Auth Middleware
5 labs
🔒
6 min
-
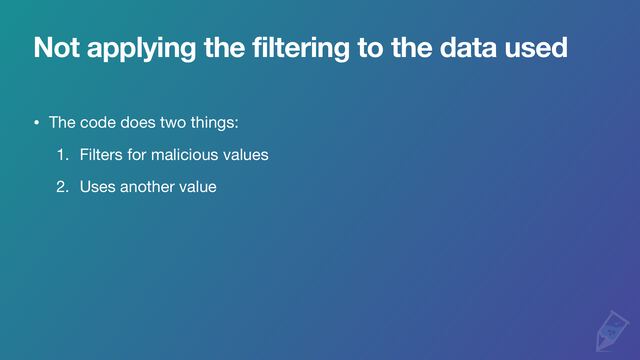 06-06
Filtering the Wrong Value, and Non-Recursive Filters
2 labs
🔒
4 min
-
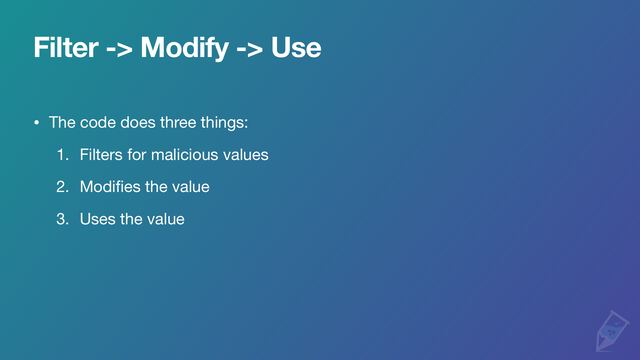 06-07
Filter, Then Modify
🔒
7 min
-
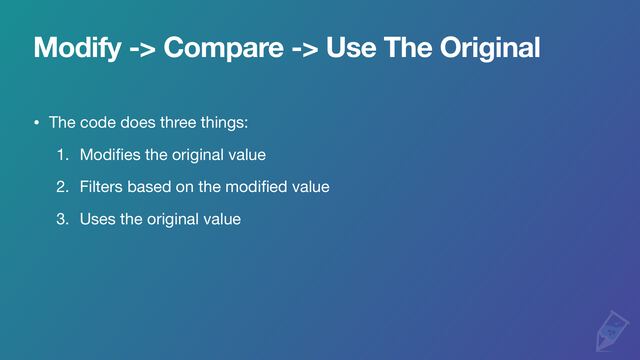 06-08
Compare One Value, Use Another: Uppercase, Unicode and Reused Emails
1 lab
🔒
5 min
-
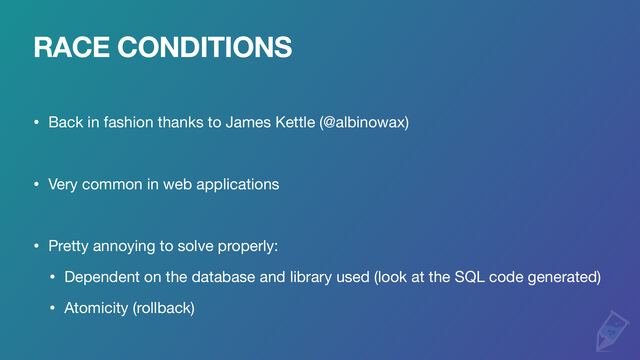 06-09
Race Conditions: Claiming a Gift Twice, and Locking It
🔒
6 min
-
 06-10
TOCTOU: DNS Rebinding and Redirects
🔒
4 min
-
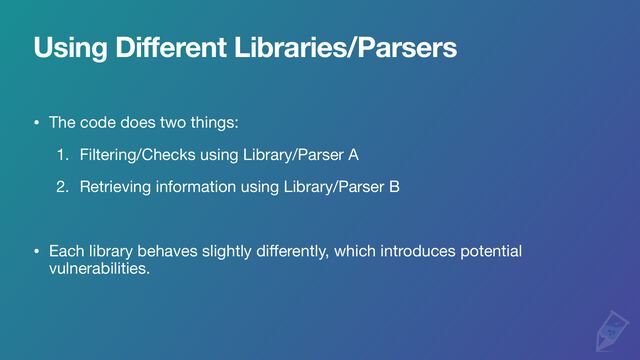 06-11
Parser Differentials, and Components That Disagree
2 labs
🔒
5 min
-
 06-12
Your Turn: The H2 Filter Bypass
🔒
7 min
-
 06-13
Reinventing the Wheel: Play's Session Injection
2 labs
🔒
7 min
7Gotchas: Tricks and Traps
-
 07-01
What Gotchas Are, and Two C# Path Traps
🔒
5 min
-
 07-02
PHP Traps That Modern Versions Killed
1 lab
🔒
6 min
-
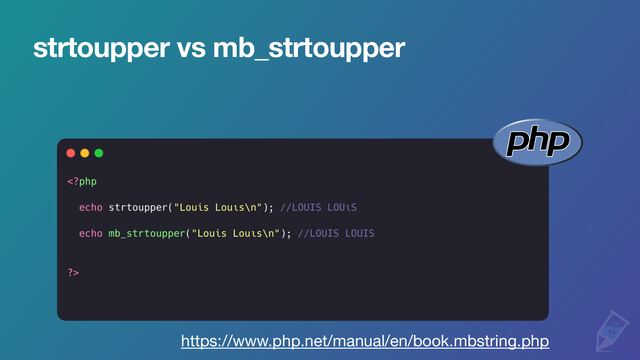 07-03
PHP's Modern Traps, and Your Turn with openssl_verify
1 lab
🔒
8 min
-
 07-04
Python Gotchas: join, urljoin, pickle, re.match and XML
1 lab
🔒
6 min
-
 07-05
Your Turn: Bokeh's WebSocket Origin Bypass (CVE-2026-21883)
1 lab
🔒
4 min
-
 07-06
Python: assert Is Not a Security Check (vLLM, CVE-2026-41523)
🔒
4 min
-
 07-07
Go: path.Clean and Upload File Names
2 labs
🔒
4 min
-
 07-08
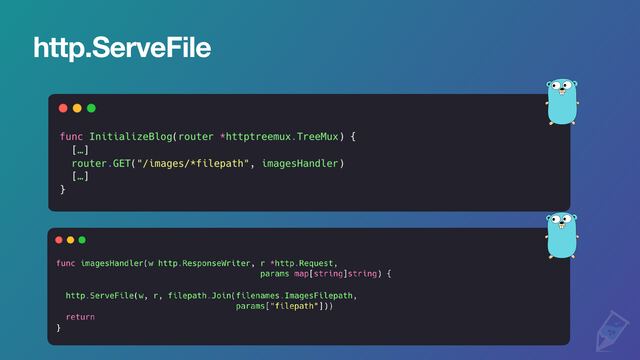
Go: ServeFile and the Safer File APIs
🔒
6 min
-
 07-09
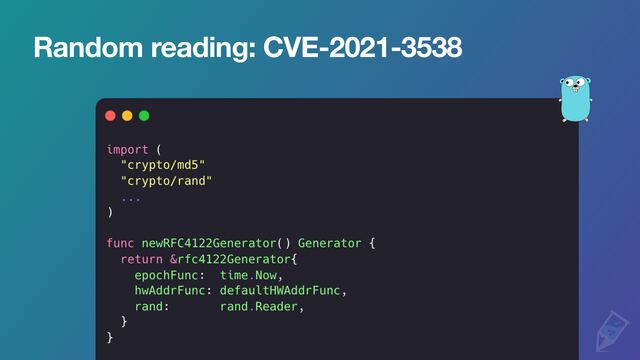
Go: Read vs io.ReadFull, the go.uuid Bug
1 lab
🔒
5 min
-
 07-10
Go: hash.Sum, Client Certificates and Loop Variables
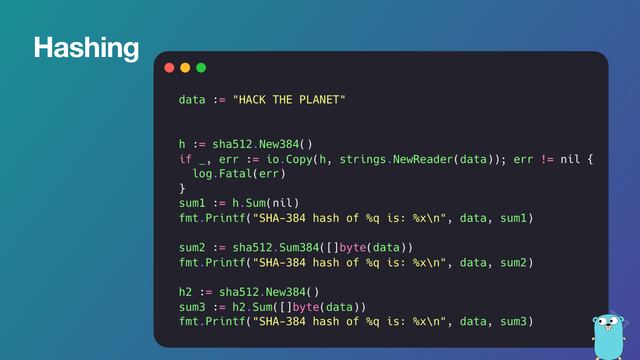
2 labs
🔒
8 min
-
 07-11
Java: URL Parsing, and When null Becomes "null" (Tomcat)
1 lab
🔒
6 min
-
 07-12
JavaScript Oddities and Prototype Pollution
1 lab
🔒
5 min
-
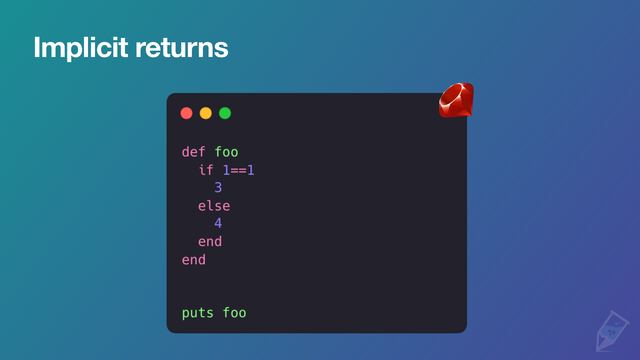 07-13
Ruby: Implicit Returns, Truthiness, Regex Anchors and Kernel open
1 lab
🔒
7 min
-
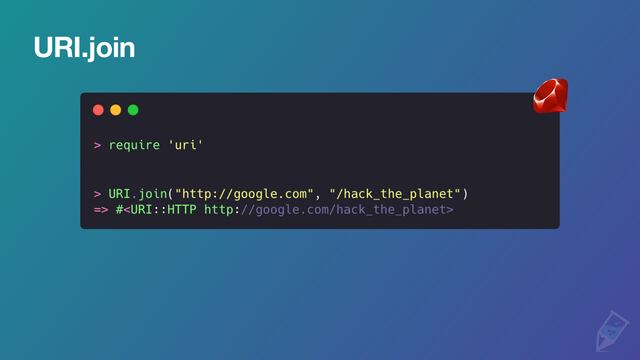 07-14
Ruby: URI.join, REXML and Mass Assignment, Then Finding Your Own Gotchas
1 lab
🔒
6 min
8CVE Analysis
-
 08-01
Why Analyse CVEs, and Where to Find Them
🔒
4 min
-
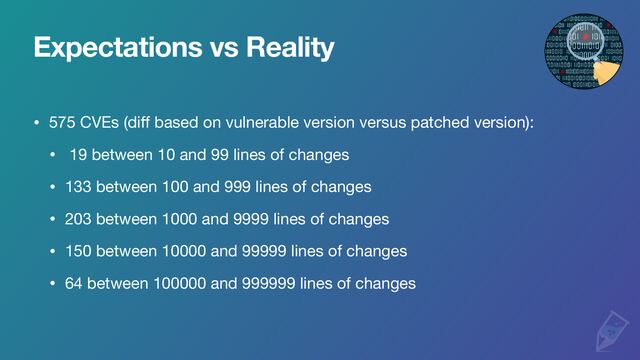 08-02
What a Real Patch Looks Like, and the Workflow
🔒
3 min
-
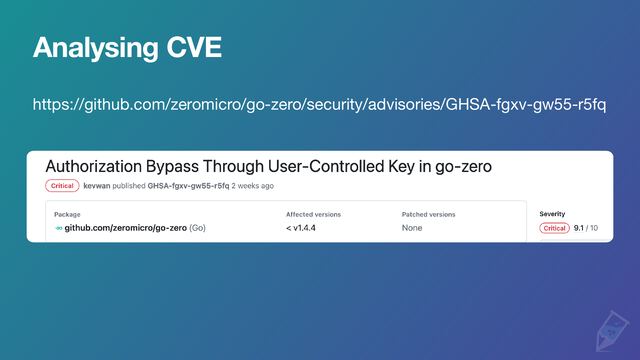 08-03
Reading a Fix: go-zero's CORS Bypass, Then Your Turn
1 lab
🔒
5 min
-
 08-04
Signed, Then Forged: WordPress Cookies (CVE-2008-1930)
1 lab
🔒
5 min
-
 08-05
Same Parameter, Two Functions: Concourse (CVE-2022-31683)
1 lab
🔒
4 min
-
 08-06
startsWith Is Not Path-Aware: Apache James (CVE-2021-40525, CVE-2022-22931)
1 lab
🔒
5 min
-
 08-07
When Lowercasing Changes the Length: FrankenPHP (CVE-2026-24895)
1 lab
🔒
5 min
-
 08-08
Bypassing the Fix: FrankenPHP's Unicode Fallback (CVE-2026-45062)
🔒
3 min
9Tools
-
 09-01
Sizing and Navigating a New Codebase
🔒
7 min
-
 09-02
Open-Source Scanners: graudit, and Scanning Every Diff
🔒
4 min
-
 09-03
Semgrep and CodeQL
🔒
5 min
-
 09-04
Dependencies and Project Health
🔒
3 min
-
 09-05
Docker as a Code-Review Workbench
🔒
6 min
-
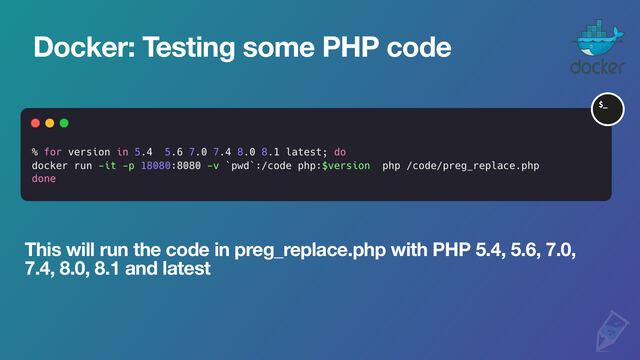 09-06
Testing Behaviour Across Language Versions
🔒
5 min
-
 09-07
Your Turn: A Python Version Loop
🔒
5 min
-
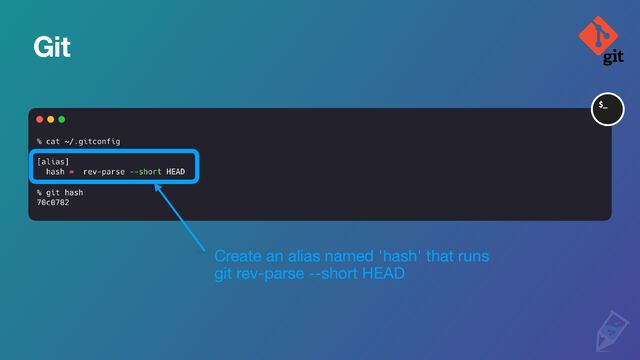 09-08
Git Archaeology for Reviewers
🔒
3 min
-
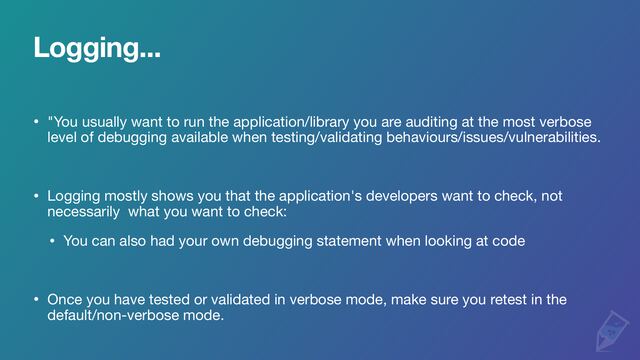 09-09
Logging and Tracing
🔒
4 min
-
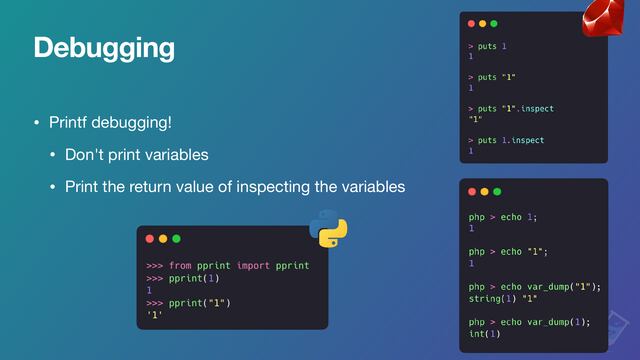 09-10
Debuggers, and Debugging a Real CVE
🔒
7 min
-
 09-11
Buying a Commercial SAST
Bonus
🔒
8 min
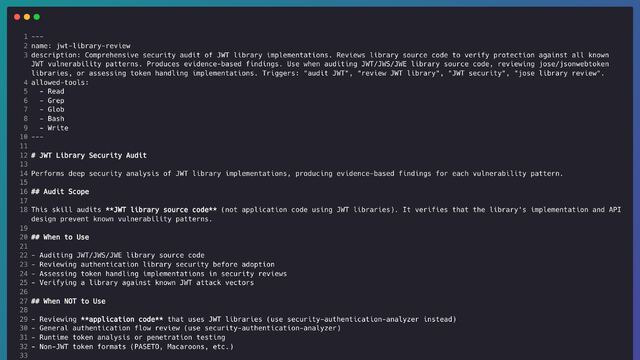
10AI-Assisted Review
11Deep Dive: Signed Data
-
 11-01
Signed Data: The Attack Surface, and Why Encryption Isn't Enough
1 optional lab
🔒
5 min
-
 11-02
Signature Flaws: Signing Oracles, Leaks, Length Extension and Homemade Signing
2 labs
🔒
7 min
-
 11-03
Signed, but Still Broken: Thumbor's Signed URLs (CVE-2026-53501)
🔒
4 min
-
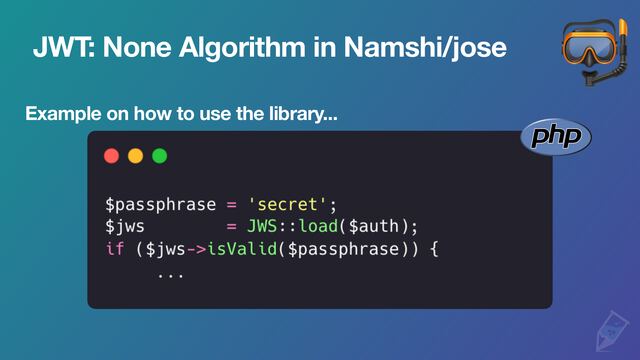 11-05
JWT: The None Algorithm, in a Real Library
1 lab
🔒
5 min
-
 11-06
JWT: Algorithm Confusion, and a Missing Default Case
2 labs
🔒
8 min
12Deep Dive: Authentication
-
 12-01
Navidrome: How an Overwritten Error Bypassed Authentication (CVE-2025-27112)
🔒
8 min
-
 12-02
Password Storage Done Well: crypto-js vs Django
🔒
9 min
-
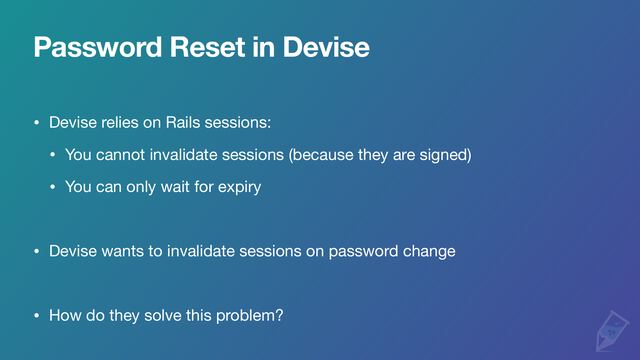 12-03
Session Invalidation and Password Reset
1 lab
🔒
4 min
-
 12-04
A Password Reset That Re-Enables Banned Accounts (Vikunja, CVE-2026-33316)
🔒
5 min
13Strategies
-
 13-01
Before You Pick a Strategy
🔒
3 min
-
 13-02
Ways to Approach a Codebase
🔒
6 min
-
 13-03
Spot the Difference, CVE-Driven, and My Usual Flow
🔒
6 min
-
 13-04
Sources and Sinks, and Where Tracing Falls Short
Bonus
🔒
6 min
-
 13-06
Hardening Compounds: What Chasing Paths Costs You
Bonus
🔒
6 min
-
 13-07
Case Study: Rails and Marshal
Bonus
2 optional labs
🔒
5 min
-
 13-08
What to Do Instead: Features, Capabilities, Patterns and Campaigns
Bonus
🔒
4 min
Prerequisites
A foundational understanding of common web vulnerabilities is required. This knowledge is crucial for understanding the vulnerabilities discussed and reviewed in the lessons.
Practical skills in managing and running Docker containers are also necessary, as part of the course uses Docker to test and explore different security scenarios. Familiarity with basic Docker commands and concepts will let you follow every hands-on activity.
About the Instructor
Louis Nyffenegger is the founder of PentesterLab, a leading educational platform renowned for its comprehensive, hands-on security labs, many of which were personally created by him. Before establishing PentesterLab, Louis honed his expertise in penetration testing across France and Australia. He subsequently specialized in security code reviews at the National Bank of Australia, followed by application security roles at Australia Post and Fitbit, where he regularly performed code reviews. Louis is also a well-regarded speaker, frequently sharing his insights at security conferences such as DEFCON, multiple OWASP events (Auckland, Brisbane, California, Melbourne, ...) and multiple BSides events (Canberra, Perth, Toronto, ...). Additionally, he runs the YouTube channel AppSecSchool, where he shares knowledge and insights on application security.