SECURE CODING IN GOLANG
The on-demand version of our Go training, designed for developers who want to write and review safer Go. Louis uses real-world Go vulnerabilities and CVEs to show how and why bugs happen, the Go quirks that catch experienced developers, the safer APIs and tools to use instead, and how to fix issues so they stay fixed, in short lessons you can watch at your own pace. Most lessons come with a PentesterLab lab, and a lesson counts as complete once you've solved its lab.
34 short lessons across 9 modules, about 2.5 hours of video. Watch at your own pace and pause when Louis asks you to look at the code. Lessons with a PentesterLab lab count as complete once you have solved the lab (labs marked optional are extra practice).
Training a team? Buy in bulk or deploy it in your LMS.
Not your basic OWASP Top 10 training
No basic bugs
A lot of secure coding trainings are based on the OWASP Top 10, with simplified snippets. This one starts where they stop: the bugs that get past experienced Go developers, and how to catch them in your own code.
Real bugs from real CVEs
The patterns come from vulnerabilities in real Go projects: an overwritten error that bypassed Navidrome's authentication, Vikunja's password reset, go-zero's CORS bypass. You read the vulnerable code, see why it was exploitable, and how it was fixed.
Complex bugs
Bugs that hide in the details: a ToLower that changes a string's length and leads to code execution in FrankenPHP, then the bypass of its fix; SSRF checks that fall to DNS rebinding; a gift you can claim twice with a race condition.
That's what this course is for: how real Go vulnerabilities happen, the Go quirks that catch experienced developers, the safer APIs to use instead, and how to fix bugs so they stay fixed.
Course Content
1Getting Started
2Patterns: Secrets, Trust and Races
-
 02-01
Secrets in Go: Hardcoded Keys and Bad Defaults
1 lab
🔒
3 min
-
 02-02
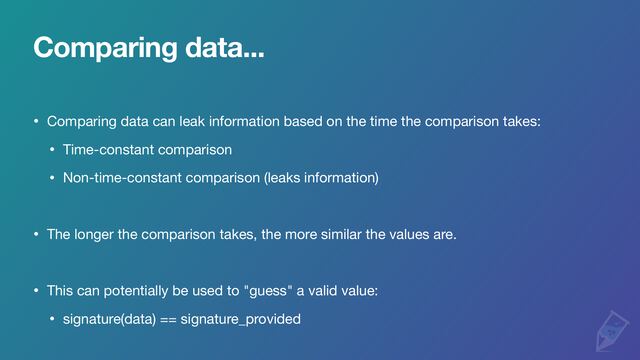
Comparing Secrets: Timing Attacks and Constant-Time Compare
1 lab
🔒
5 min
-
 02-03
Signing Oracles: One Signature, Two Features
1 lab
🔒
3 min
-
 02-04
Data You Shouldn't Trust, and Zip Slip
1 lab
🔒
2 min
-
 02-05
TOCTOU and DNS Rebinding, and Fixing SSRF Checks in Go
🔒
6 min
-
 02-06
Race Conditions: Claiming a Gift Twice, and Locking It with GORM
🔒
7 min
3Patterns: Filtering, Matching and Logic
-
 03-01
Filtering the Wrong Value, and Filter Then Modify
1 lab
🔒
6 min
-
 03-02
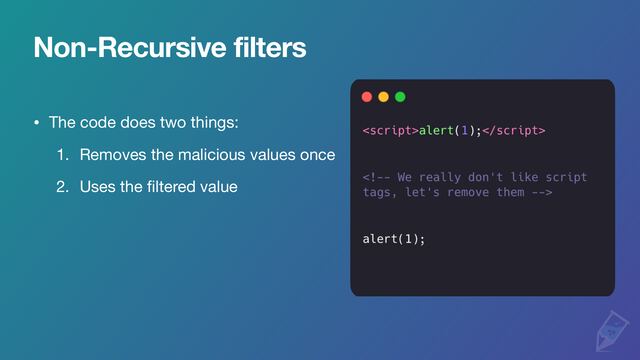
Non-Recursive Filters
🔒
3 min
-
 03-03
Modify, Compare, Use the Original: ToUpper and Unicode in Go
🔒
4 min
-
 03-04
Matching Is Hard: Contains, HasPrefix and an Empty-String CORS Bug
1 lab
🔒
5 min
-
 03-05
Regular Expressions: Unescaped Dots, Missing Anchors and [A-z]
🔒
4 min
-
 03-06
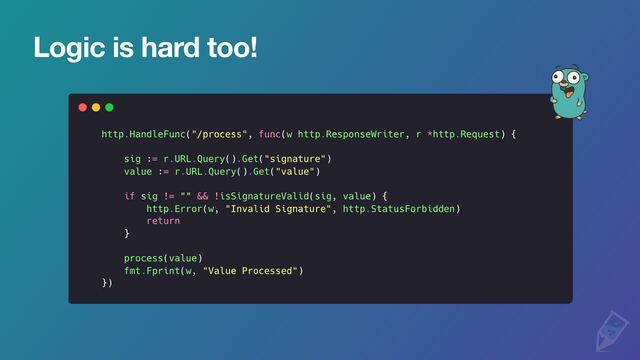
Logic Is Hard: Optional Signatures, || vs &&, and the Wrong URL Value
1 lab
🔒
5 min
-
 03-07
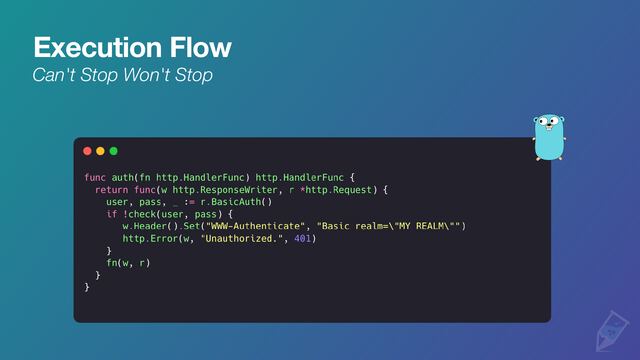
Execution Flow: Missing Returns, then Your Turn with the Auth Middleware
1 lab
+5 optional
🔒
5 min
4Go Quirks and Safer APIs
-
 04-01
path.Clean and Upload File Names: Go's Path Traps
2 labs
🔒
4 min
-
 04-02
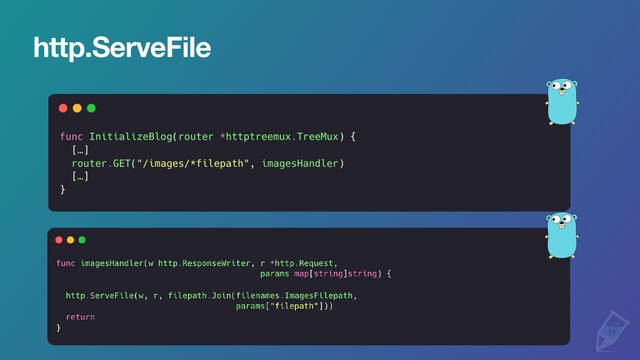
Serving and Opening Files Safely: ServeFile, IsLocal and os.Root
🔒
6 min
-
 04-03
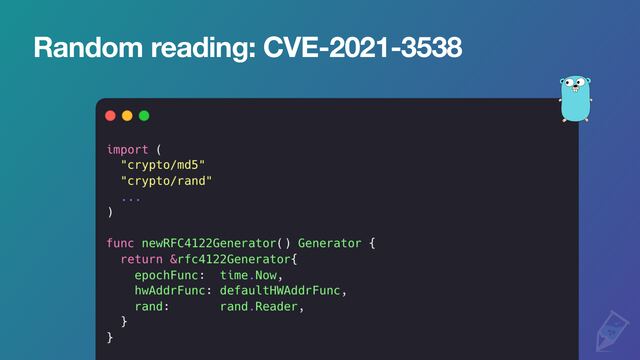
Read vs io.ReadFull: The go.uuid Randomness Bug
1 lab
🔒
5 min
-
 04-04
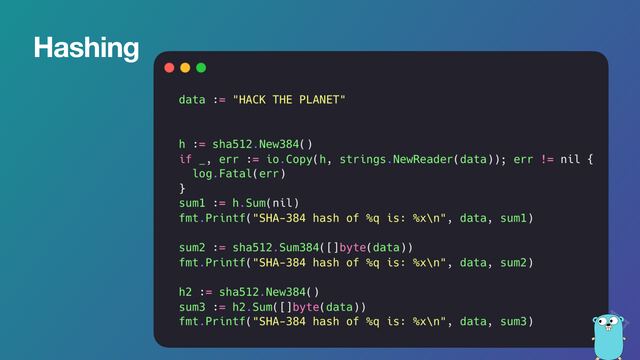
hash.Sum and Client Certificates: Go Crypto API Traps
2 labs
🔒
6 min
-
 04-05
PATH Lookups and Loop Variables: Bugs Newer Go Kills
🔒
5 min
5Learning from Real Go CVEs
-
 05-01
Learn from other people's bugs: which Go CVEs to read, and where
🔒
5 min
-
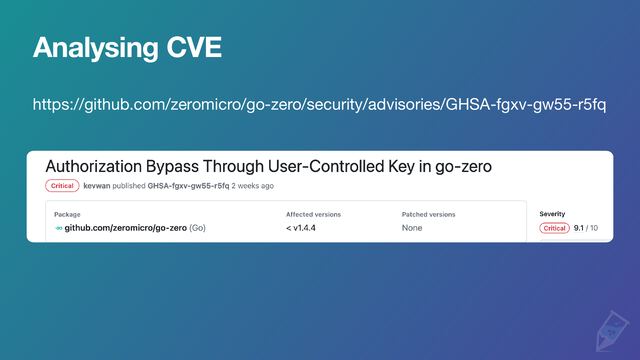 05-02
Reading a Fix: go-zero's CORS Bypass
1 lab
🔒
4 min
-
 05-03
Your Turn: Two Go CVEs (Coder and play-with-docker)
1 lab
🔒
3 min
-
 05-04
When ToLower changes the length: FrankenPHP code execution (CVE-2026-24895)
1 optional lab
🔒
5 min
-
 05-05
Bypassing the Fix: FrankenPHP's Unicode Fallback (CVE-2026-45062)
🔒
3 min
-
 05-06
Same parameter, two functions: FormValue vs URL.Query (CVE-2022-31683)
1 lab
🔒
5 min
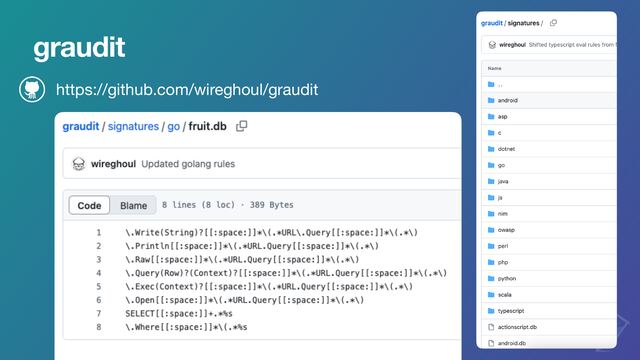
6Tools for Go Code Review
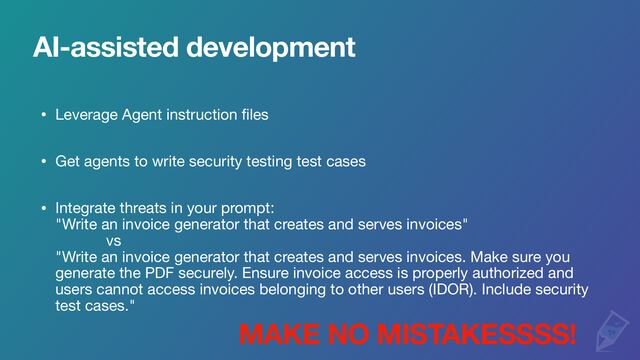
7AI-Assisted Development
8Defensive Programming
9Remediation and Conclusion
Prerequisites
A foundational understanding of common web vulnerabilities, as this knowledge will be essential for fully grasping the security concepts discussed in the lessons.
Working knowledge of Go. Familiarity with basic git commands helps too, as the CVE analysis lessons compare vulnerable and fixed versions with git.
About the Instructor
Louis Nyffenegger is the founder of PentesterLab, a leading educational platform renowned for its comprehensive, hands-on security labs, many of which were personally created by him. Before establishing PentesterLab, Louis honed his expertise in penetration testing across France and Australia. He subsequently specialized in security code reviews at the National Bank of Australia, followed by application security roles at Australia Post and Fitbit, where he regularly performed code reviews. Louis is also a well-regarded speaker, frequently sharing his insights at security conferences such as DEFCON, multiple OWASP events (Auckland, Brisbane, California, Melbourne, ...) and multiple BSides events (Canberra, Perth, Toronto, ...). Additionally, he runs the YouTube channel AppSecSchool, where he shares knowledge and insights on application security.